The Calendar Invite That Steals Trust
2026-10-11
Calendar phishing borrows institutional authority. An appointment or renewal reminder, appearing among ordinary commitments, can direct its recipient to a counterfeit Google, Microsoft or PayPal login page that collects whatever credentials are entered. The setting supplies credibility. Unlike an unsolicited message that announces itself as an interruption, the calendar entry presents a demand as something already scheduled and therefore already accepted.
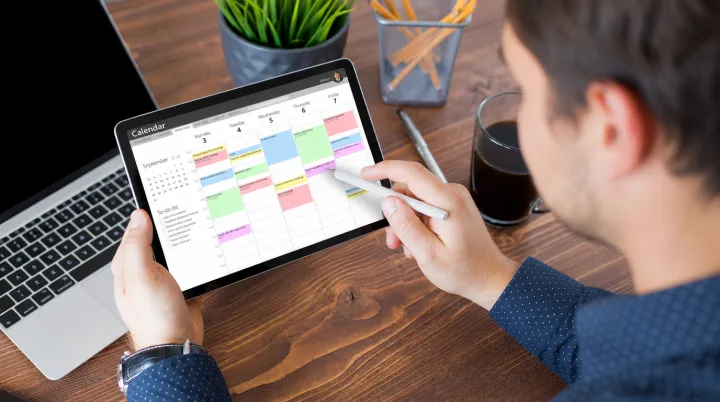
The deception exploits misplaced trust. Depending on calendar settings, invitations from unfamiliar senders may appear automatically, allowing an attacker to place a link where recipients expect meetings rather than sales pitches. Familiar branding does the rest. Credential harvesting, the collection of passwords through imitation login forms, can enable account takeover when stolen details work and additional authentication does not stop access. A reminder becomes a lever. Reports describing exponential growth deserve scrutiny, because that mathematical claim requires comparable measurements over successive periods, not merely evidence that more malicious invitations are circulating.
Independent verification beats visual reassurance. Open the service through its app or a saved bookmark rather than through the event, and check whether the supposed appointment, payment or renewal actually exists. Treat invitations as unverified requests. Review settings that automatically add events from unknown senders, report suspicious entries, and use phishing-resistant authentication such as passkeys where available. Password changes alone have limits. If credentials were entered, change them through the genuine service, review account activity and revoke unfamiliar sessions, since access may persist after a password reset. The trap is borrowed certainty. On the screen, the fraudulent appointment occupies exactly as much space as a real one.
Loading...